For financial services, fintechs and SACCOs
Governance discipline for regulated boards.
Banks, microfinance institutions, fintechs and SACCOs operate under close scrutiny. Diranta helps boards and management keep decisions, declarations, policies and strategy delivery evidenced and under control.
The challenge
Regulated boards need evidence, not just minutes.
Boards and committees must show how decisions were made, who was conflicted and which policies directors have read, while executing a demanding strategy.
Many committees
Conflicts and declarations
Policy attestation
How Diranta helps
Evidenced governance and disciplined execution.
Diranta keeps the governance record complete and connects the board's decisions to the initiatives that carry them out.
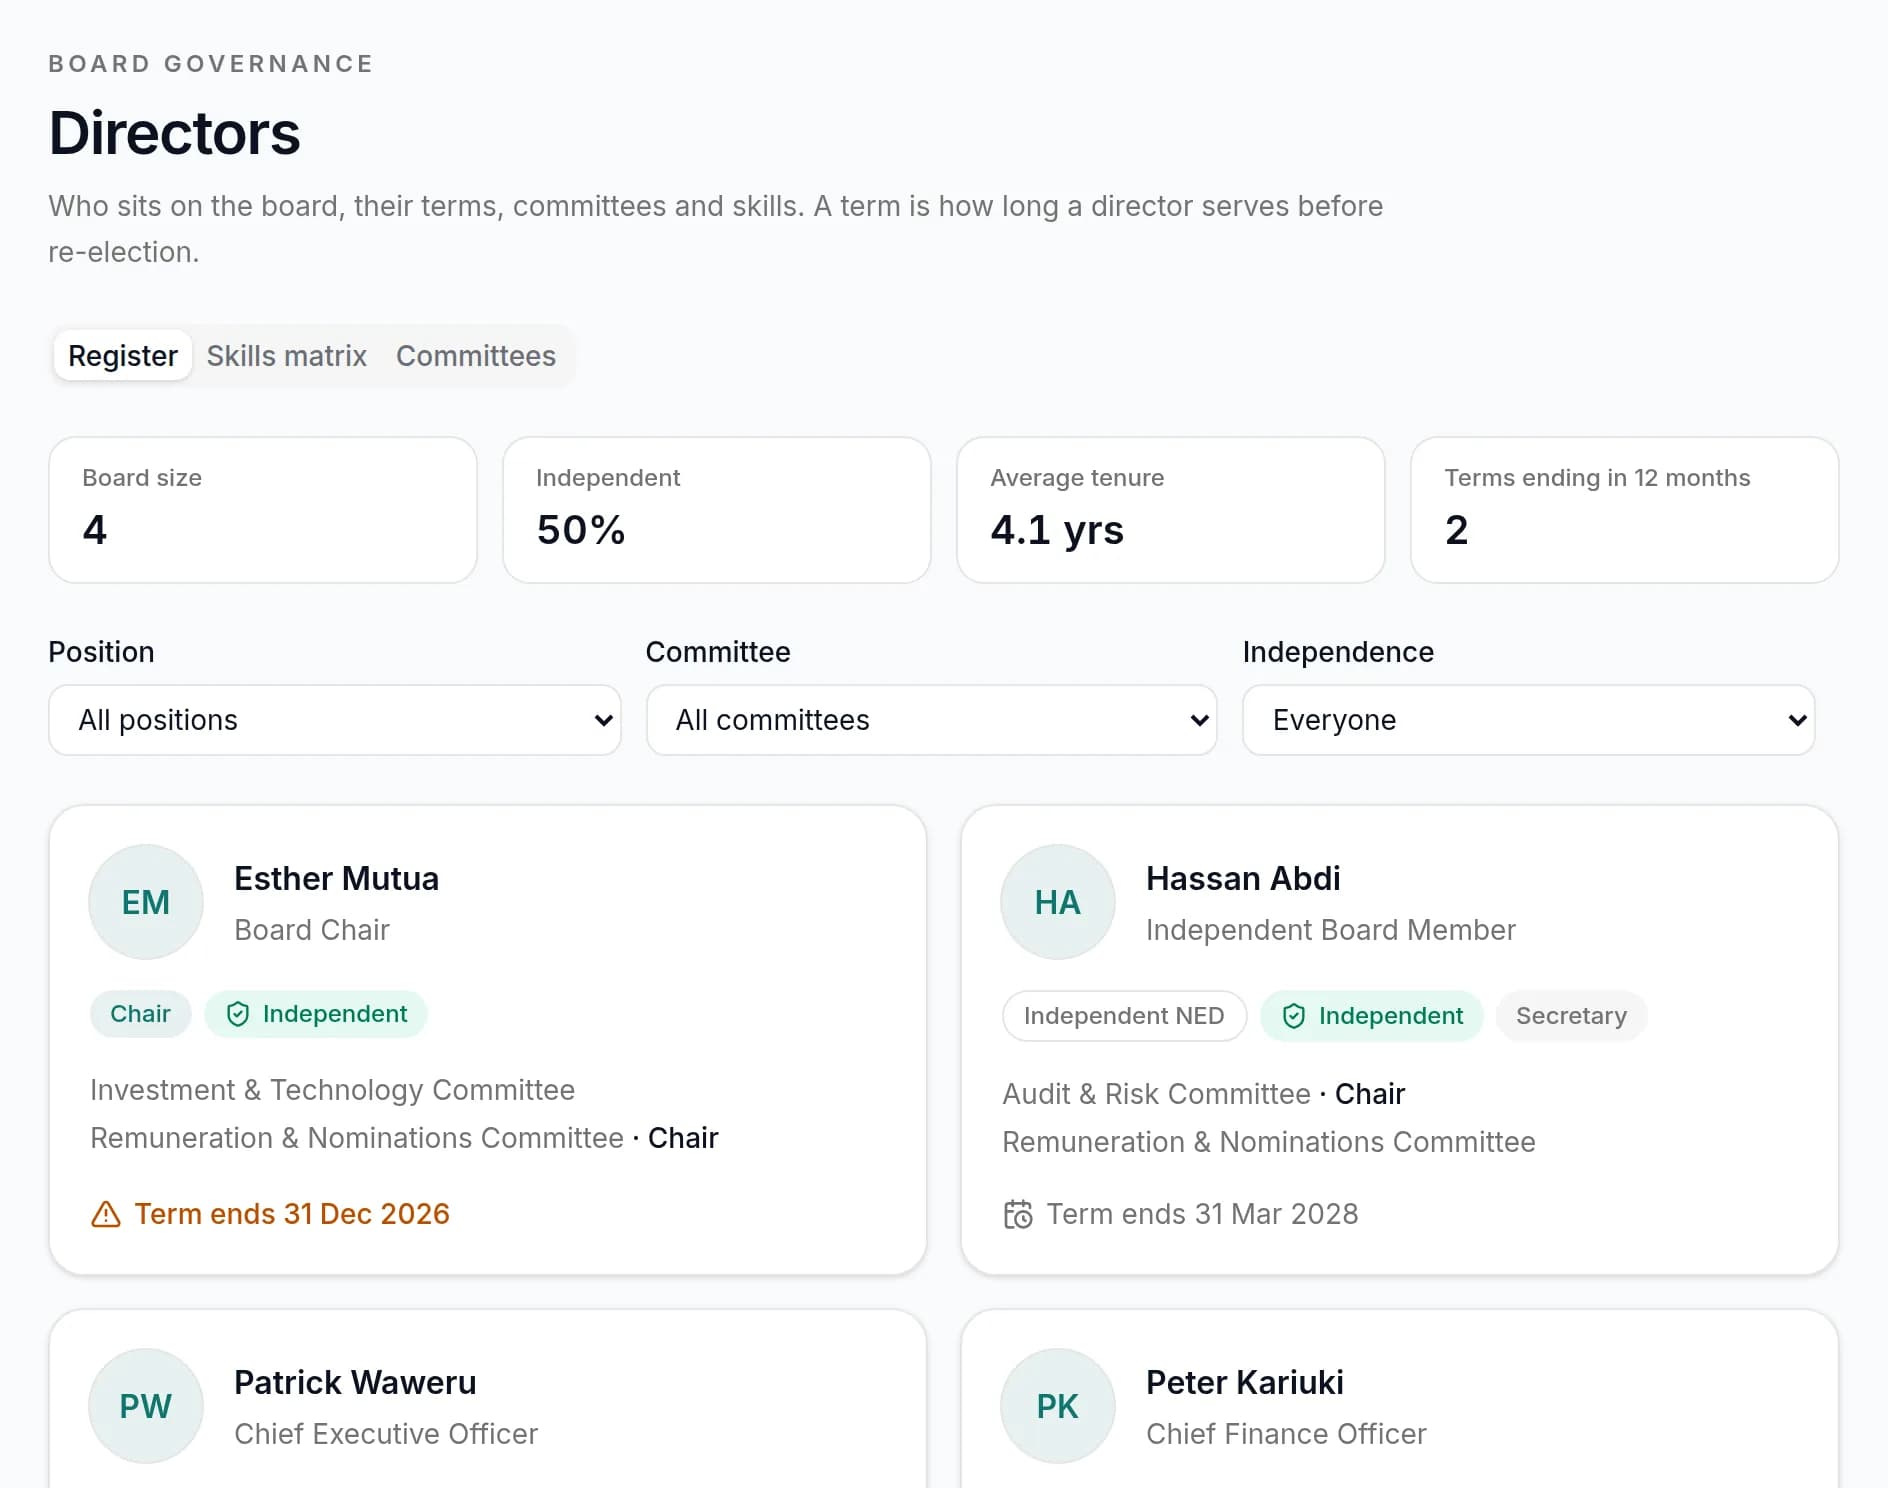
Governance registers
Declarations, skills and policies in one record.
Maintain the director register and skills matrix, run declaration-of-interest rounds and publish policies for acknowledgement with reminders and version history.
- Interests register and conflict confirmations
- Policy library with acknowledgements
- Board evaluations and director questionnaires
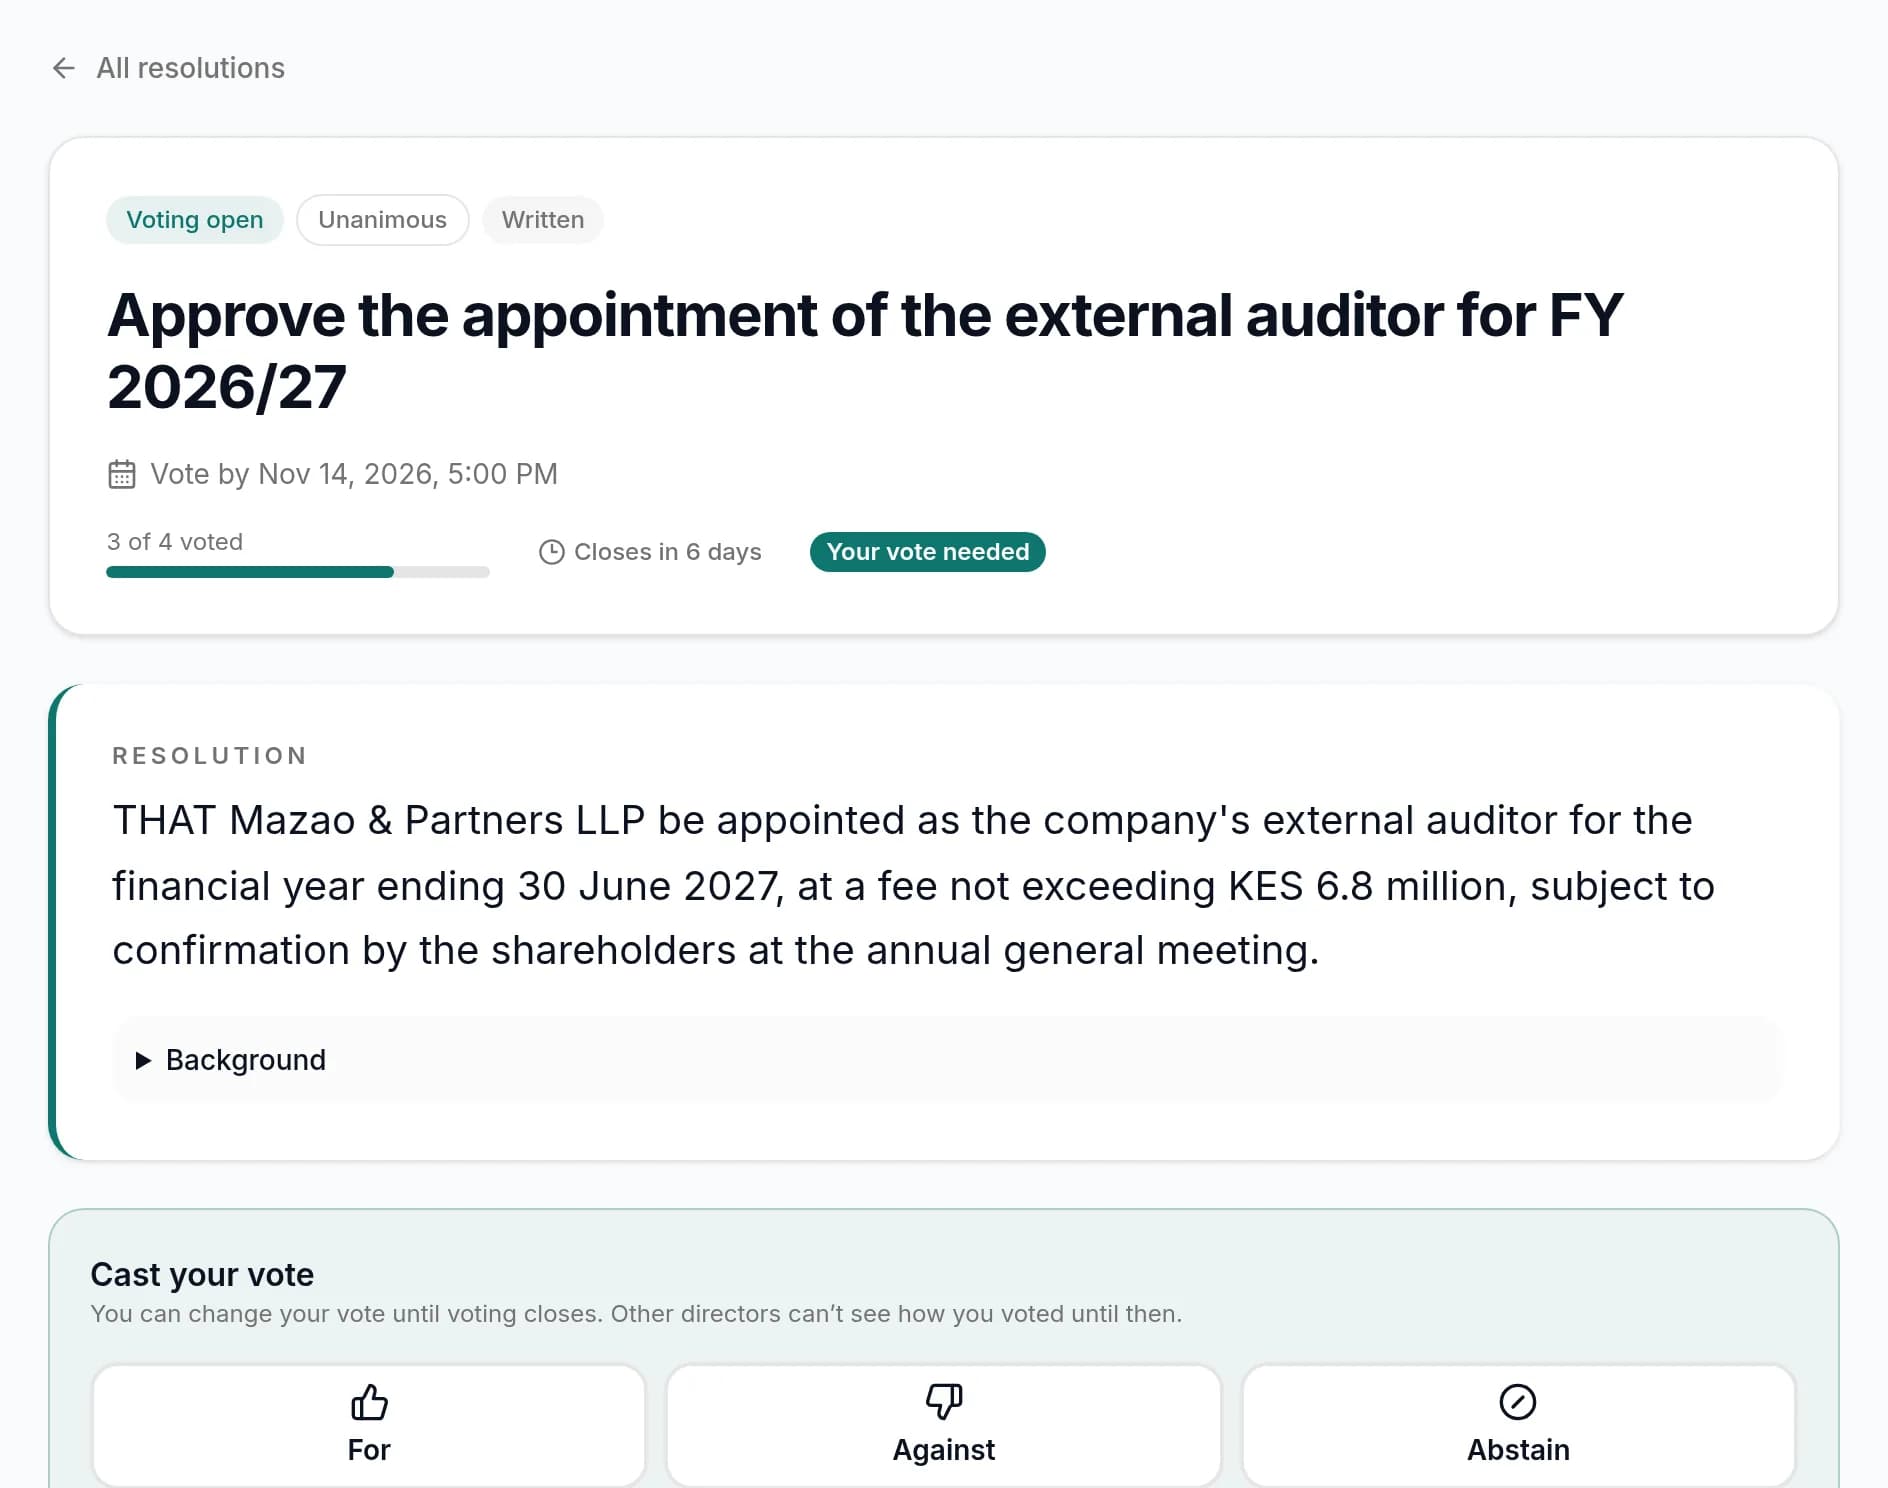
Decisions
Resolutions with conflicts excluded automatically.
Directors with a declared conflict are excluded from voting on the relevant resolution. Outcomes, reference numbers and signatures are kept together in the resolution register.
- Meeting and written resolutions
- Reference numbering in sequence
- Built-in e-signatures
Strategy delivery
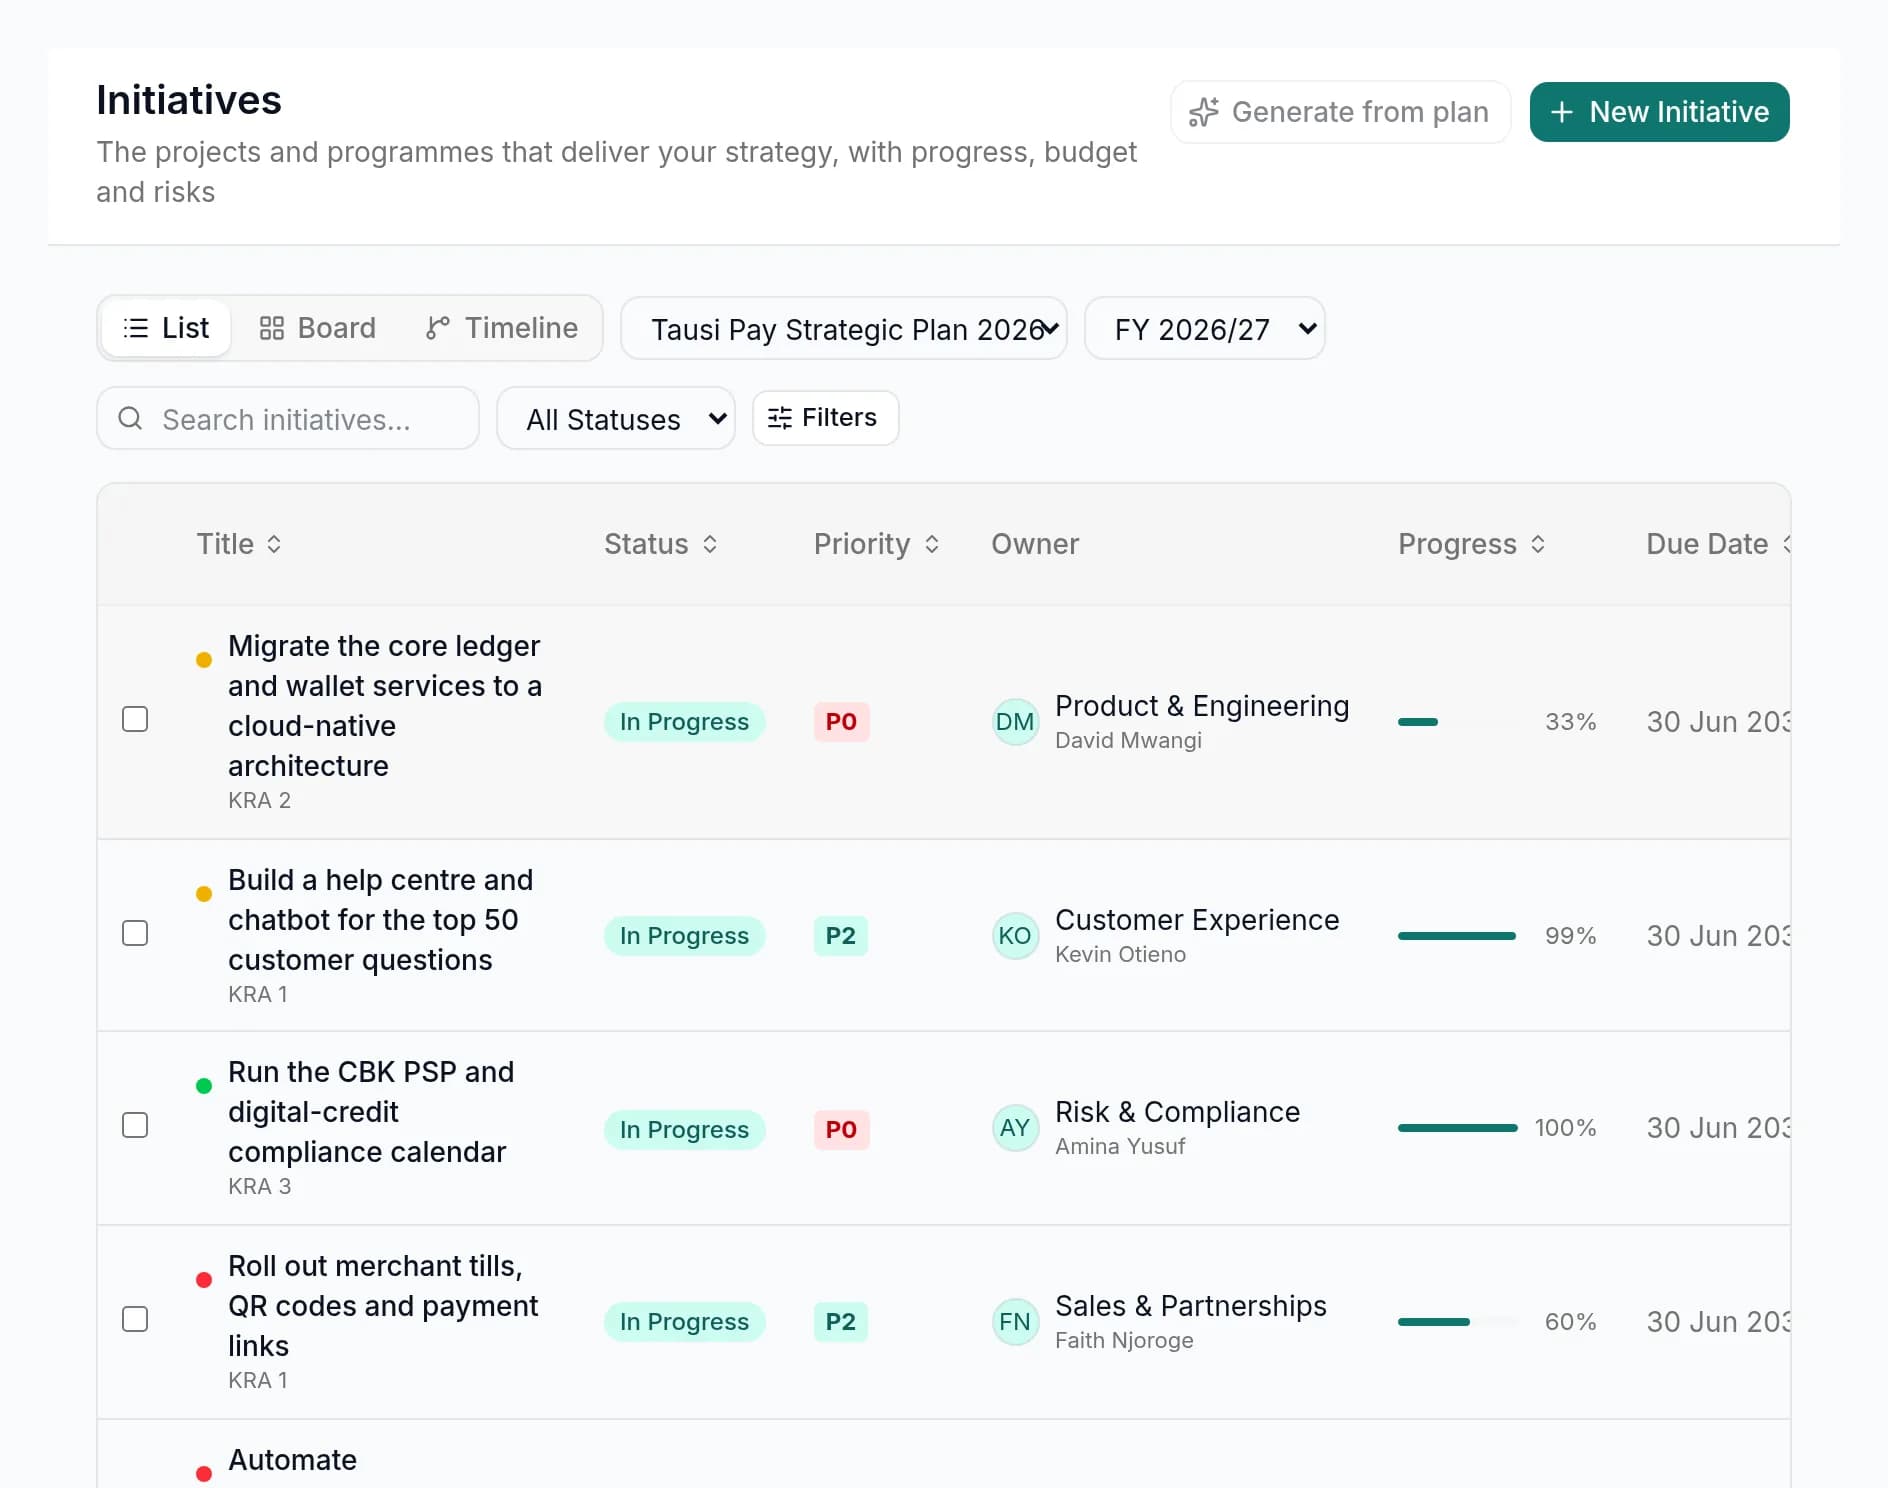
Initiatives with budgets and risks in view.
Track the strategic initiatives that matter, such as product launches, core-system upgrades and branch expansion, with milestones, spend approvals and likelihood-and-impact risk registers.
- Budgets and spend approvals
- Risk scoring and mitigation status
- Quarterly OKRs from strategic KPIs
Security
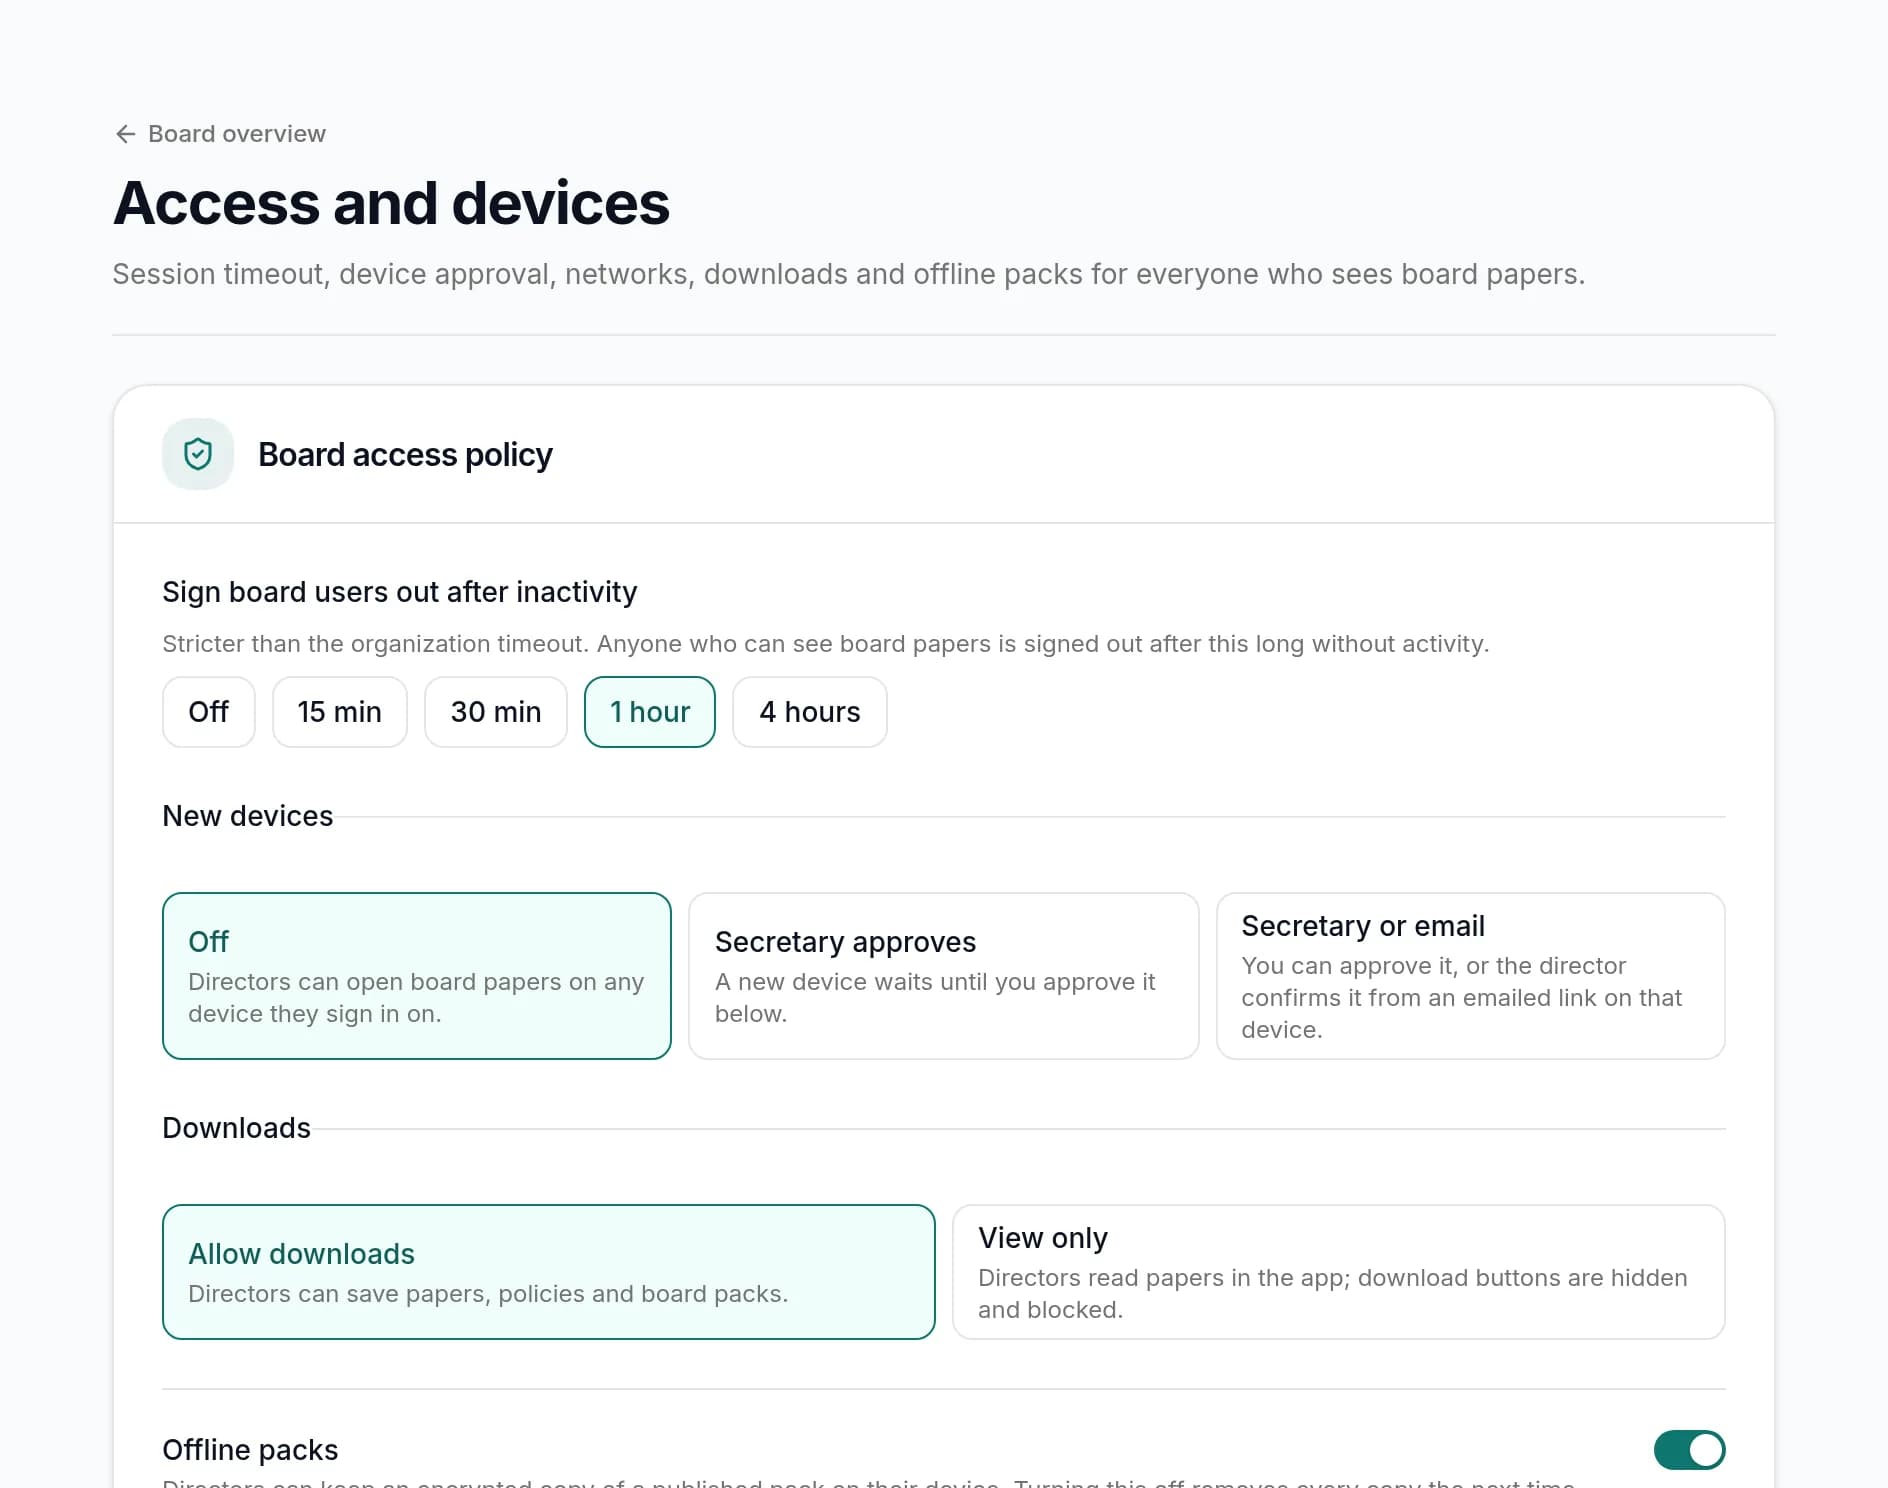
Controls proportionate to the sensitivity.
Require two-factor authentication, enforce single sign-on, approve board devices, restrict access by IP and keep a hash-chained audit log of governance activity.
- 2FA and OIDC single sign-on
- Device approval, IP allowlists and remote wipe
- Tamper-evident audit log
What you get
What financial-services boards use Diranta for.
Committee portals
Declarations of interest
Policy acknowledgements
Resolution register
E-signatures
Risk registers
Budget control
Strategy and OKRs
Board reporting
Access controls
Private AI
Audit trail
FAQ
Frequently asked questions
Can't find what you need? Our team is happy to help.
Does Diranta make us compliant with our regulator's governance requirements?
No software can do that on its own. Diranta helps you run and evidence good governance practice, such as declarations, policy acknowledgements, conflict handling and a complete decision record, which supports your compliance work.
Is Diranta suitable for SACCOs?
Yes. SACCO boards and supervisory committees use the same portal for meetings, packs, minutes, resolutions and policies, and management can run the strategic plan alongside it.
Can we restrict board access to our office network?
Yes. IP allowlists limit board access to the address ranges you specify, and device approval controls which devices directors can use.
Can policies be acknowledged by staff as well as directors?
Policies can be published to defined audiences with acknowledgement tracking and reminders. Talk to us about the audiences you need.
Bring your plan. We'll show you how it runs.
A 30-minute walkthrough using your own strategic plan or last board pack, not a generic demo.